Every new domain adds lifecycle sequencing, vCenter scope, capacity planning, monitoring, backup, certificate, access, networking, and troubleshooting work. Create a domain only when the boundary removes more risk or complexity than it introduces.
The Management Domain Is a Protected Operating Zone
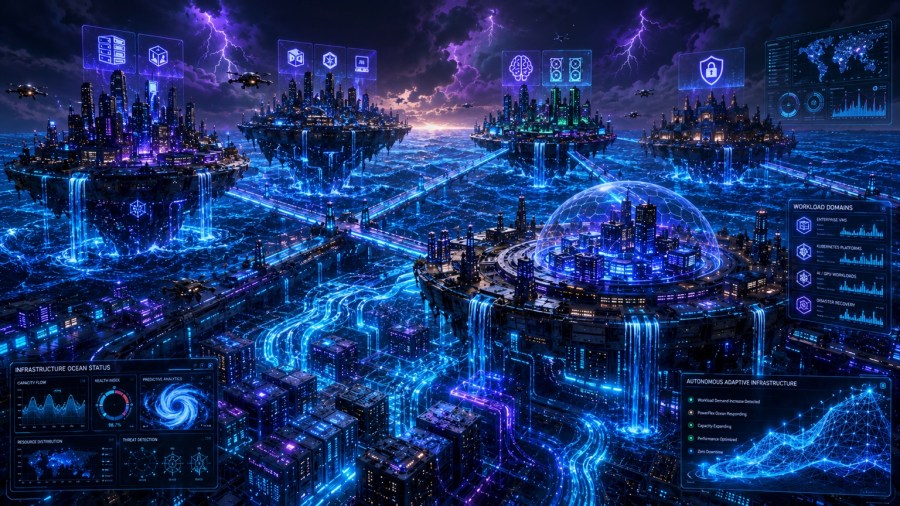
The strongest idea in the image is not the futuristic automation dashboard or the glowing data bridges. It is the deliberate coexistence of shared platform control and distinct workload operating zones.
Automation that can change infrastructure but cannot validate service outcomes is not autonomy. It is accelerated configuration change. Every automated action needs success criteria, failure handling, and evidence.
VI Workload Domains Are Infrastructure Contracts
Fleet scope covers the services and policies intended to coordinate multiple VCF instances, such as global operations, automation, identity integration, software distribution, and organization-wide governance. Not every capability must be centralized, but every centralized capability needs a clear availability and recovery design.
The term adaptive infrastructure is used carefully. It does not mean that the platform should make unrestricted production changes without human oversight. It means the operating model can observe conditions, compare them with policy, select an approved action, execute through automation, validate the result, and preserve an audit trail.
Which workload classes are allowed?
Which hardware, storage, and network profiles are approved?
Who owns capacity and lifecycle decisions?
Which security and identity controls apply?
What are the availability, recovery, and maintenance objectives?
Which services are shared with other domains?
How will drift, exceptions, and decommissioning be handled?
Recovery architecture may require a second site, another VCF instance, separate management dependencies, protected identity and DNS services, replicated data, recovery plans, tested sequencing, and a defined failback process. The domain is one building block. The recovery objective determines whether the boundary must extend to another cluster, site, instance, region, or fleet.
Four Workload-Island Patterns
Document every required cross-domain flow and shared dependency. Identify the owner, enforcement point, monitoring signal, failure behavior, and recovery method for each bridge.
Enterprise VM Domain
A VCF instance contains one management domain and can contain additional virtual infrastructure workload domains. A VCF fleet can contain one or more VCF instances and introduces a broader management scope for operations and automation. A workload domain groups application-ready infrastructure with defined characteristics and is managed through its associated vCenter boundary.
This article uses VMware Cloud Foundation 9.1 as the version baseline. It is a mental-model and design article, not a complete validated reference architecture. Hardware compatibility, component interoperability, storage support, networking patterns, licensing, and scale limits must still be checked against the current Bill of Materials, release notes, compatibility guides, and product documentation before implementation.
Kubernetes Platform Domain
Stay informed
Tenants and application teams own workload configuration, application service levels, data protection selections, application recovery steps, consumption behavior, and the use of approved platform services. Self-service changes the interface, not accountability.
AI and GPU Domain
A domain topology should be the result of a repeatable decision process, not a diagramming preference.
The best topology normally contains a small number of durable domain profiles. Applications are placed into those profiles through policy and service eligibility, rather than creating new infrastructure boundaries for every request.
Third, modern workload services remain consumers of the underlying domain design. VKS, private AI services, GPU-enabled virtual machines, and recovery tooling can use a shared private-cloud platform, but their infrastructure profiles may still justify distinct boundaries.
Recovery Domain or Recovery Instance
Treating the management domain as spare application capacity weakens the design. Even when a supported consolidated model is appropriate for a smaller environment, management workloads still need protected resources, clear placement rules, controlled change, and recovery procedures. The central city in the image is protected for a reason: when the management layer is unstable, every surrounding domain becomes harder to operate.
This approach prevents two common extremes. The first is domain sprawl , where every application or team receives an island and the platform becomes expensive to patch, monitor, secure, and capacity-plan. The second is the single-continent design , where every workload shares one operational fate and specialized requirements are handled through exceptions.
Choose Domain Boundaries by Operating Contract
VMware Cloud Foundation discussions often begin with products: vSphere, vSAN, NSX, VCF Operations, VCF Automation, and the services layered above them. That product view matters, but it does not explain the most important architecture decision in a real deployment: where the private cloud should be divided into independently managed operating zones.
Boundary signal
Favor a separate domain when
Favor a shared domain when
Lifecycle
Upgrade cadence, maintenance windows, or compatibility requirements differ materially
Components can move through the same validated lifecycle
Hardware
GPU, storage, network, CPU, or compliance-certified hardware is specialized
Hosts are operationally interchangeable
Security
Administrative, tenant, trust, inspection, or data-residency boundaries differ
Common controls and ownership are sufficient
Availability and recovery
RTO, RPO, failure-domain, or maintenance requirements need distinct treatment
Services share the same resilience profile
Capacity
Contention must be isolated or reserved capacity must be protected
Shared capacity improves utilization without unacceptable risk
Ownership
Different teams have clear accountability and change authority
A single platform team operates the environment consistently
Cost and licensing
Chargeback, accelerator economics, or software placement needs a distinct pool
Shared placement does not distort cost or licensing decisions
Dependency density
Cross-domain traffic can remain limited and well governed
Heavy coupling would turn the boundary into administrative friction
Second, an API-first interface does not remove dependency management. Automation clients, Terraform configurations, PowerCLI modules, Python integrations, and internal workflows still need version control, compatibility testing, access policy, error handling, and rollback.
Finally, brownfield adoption does not remove the need to rationalize existing vCenter and cluster boundaries. Import and convergence capabilities can bring existing infrastructure under VCF management, but architects should still decide whether the inherited topology represents the target operating model or merely the current state.
Adaptive Infrastructure Is a Closed Operational Loop
APIs and workflows should implement the approved domain contract. They should not be used to hide unclear ownership or unresolved design decisions. Version pinning, prechecks, staged rollout, rollback, and evidence collection remain part of the automation design.
A VCF workload domain should exist because a group of workloads needs a distinct infrastructure contract, such as a different lifecycle cadence, hardware profile, security boundary, recovery objective, capacity model, or ownership structure. Enterprise VMs, Kubernetes platforms, AI/GPU services, and recovery capacity may justify separate domains, but workload type alone is not enough. The design goal is not maximum separation. It is controlled independence with explicit shared services, governed connectivity, and measurable operational outcomes.
The workload types shown in the image are practical domain-design candidates, but they are not mandatory one-to-one mappings. The correct topology depends on nonfunctional requirements and operating constraints.
A VI workload domain groups one or more clusters around a defined set of characteristics. Each domain has an associated vCenter management boundary, while networking can follow supported shared or separated designs. The important point is not the number of clusters. It is the consistency of the operating contract across those clusters.
The same loop can support certificate renewal, password rotation, image compliance, drift remediation, patch planning, or service provisioning. The controls should become stricter as the potential blast radius increases. A low-risk catalog deployment can be highly automated. A fleet-wide lifecycle change still needs staged execution, prechecks, change gates, and recovery planning.
Fleet Scope
For each proposed domain, record:
Instance Scope
A practical example is capacity expansion. Demand increases in the AI domain. Telemetry identifies sustained accelerator pressure. Policy confirms that the threshold and budget conditions have been met. An approved workflow adds or assigns capacity. Validation confirms host health, network readiness, cluster state, licensing, and workload placement. The outcome is recorded for cost and capacity planning.
Domain Scope
Test site loss, management-service degradation, network isolation, identity failure, certificate expiration, capacity exhaustion, failed upgrades, and recovery sequencing. The topology should explain how operators detect the problem, contain it, continue essential services, and restore control.
Tenant and Application Scope
AI infrastructure often creates the strongest case for a dedicated domain because accelerator hardware, high-speed networking, data access, driver compatibility, capacity economics, and security requirements can diverge sharply from general-purpose virtualization.
An AI/GPU domain can establish a controlled landing zone for deep learning virtual machines, GPU-enabled Kubernetes clusters, inference services, model-development environments, or private AI services. The boundary can also make expensive capacity visible, protect accelerator availability, and isolate changes that depend on specialized firmware, drivers, device profiles, and networking.
Where the Archipelago Model Breaks Down
A useful workload-domain contract should answer:
Too Many Islands
The operating model should also name the bridges explicitly: identity, DNS, NTP, certificate authorities, backup targets, logging, monitoring, repositories, automation endpoints, service registries, external networks, and support escalation. A shared service without an owner is an unplanned common failure domain.
One Giant Island
Use lifecycle, hardware, trust, availability, capacity, ownership, cost, and dependency density to determine whether a separate domain is justified. Record the decision and the conditions that would cause it to be revisited.
Ungoverned Bridges
Get Paul Bryant’s practical guides to enterprise AI, hybrid platforms, and day-2 operations by email. New articles as they publish. Unsubscribe anytime.
False Autonomy
First, central visibility should not be confused with identical service levels. The platform can observe several domains through a common operations layer while each domain retains different performance, lifecycle, and recovery objectives.
Capacity Islanding
A workable ownership model separates responsibilities by scope:
Recovery Inside the Same Failure Domain
The management domain is the special-purpose foundation for the VCF instance. It supports the components and relationships required to operate the environment. That makes its availability, capacity reservation, backup, certificate lifecycle, identity integration, monitoring, and recovery posture materially different from a general application landing zone.
A Practical Workload-Domain Design Sequence
The design question is not, “What kind of workload is this?” The better question is, “What must be operated differently for this workload to meet its service objectives?”
The key lesson is that a workload domain is not simply a collection of clusters with a convenient label. It is a deliberate boundary around infrastructure characteristics and operational responsibility.
Build Workload Profiles
A Kubernetes-oriented domain can provide a governed foundation for VMware vSphere Kubernetes Service clusters and the supporting platform capabilities around them. The design focus shifts from individual virtual machines to namespaces, cluster lifecycle, container networking, registries, policy, observability, and platform-team service levels.
Score the Boundary Signals
Done well, the result is not a collection of infrastructure silos. It is a private cloud that can support traditional applications, Kubernetes platforms, AI services, and recovery operations through one governed architecture while preserving the boundaries that make production operations manageable.
Map Shared Services and Traffic
Dedicated hardware protects service levels, but it can also strand expensive capacity. AI and GPU domains need utilization targets, quota policy, reservation rules, and a process for rebalancing or expanding resources.
Define the Domain Charter
The uploaded image gives us a better starting point. It shows several illuminated cities rising from a shared infrastructure ocean. Each city has a different purpose. One represents traditional enterprise systems, another modern application platforms, another AI, and another security or recovery. A protected central city coordinates the environment while telemetry panels watch capacity, health, threats, and demand.
Purpose and allowed workload classes
Accountable platform owner
Hardware, storage, and network profile
Security and identity boundary
Lifecycle and maintenance cadence
Capacity reservation and growth model
Availability, RTO, and RPO objectives
Backup and recovery dependencies
Required shared services
Automation and self-service interfaces
Monitoring, cost, and compliance evidence
Exit, consolidation, or decommission criteria
Validate the Topology Against Failure
The recovery city in the image needs the strongest terminology guardrail. A separate domain can reserve recovery capacity or isolate protection components, but disaster recovery is not achieved merely by creating another workload domain inside the same failure boundary.
Automate Only After the Contract Is Clear
Instance scope includes the management domain, core VCF relationships, instance lifecycle, platform certificates, backups, and the dependency chain required to operate the local domains. This is the level where architects should document what happens when management services are degraded but workloads continue running.
Operational Implications for VCF 9.1
The metaphor is useful, but it can encourage weak designs if taken too literally.
Define the services and standards that should remain consistent across the private cloud: identity, naming, time, certificate trust, logging, monitoring, configuration evidence, backup policy, security baselines, and lifecycle governance.