Request, Aggregate, Bypass: How Attackers Can Evade LLM Safety Classifiers
Cross-request semantic accumulation (flagging when an API key’s recent requests jointly cover a harmful-composition template) is…
Cross-request semantic accumulation (flagging when an API key’s recent requests jointly cover a harmful-composition template) is…
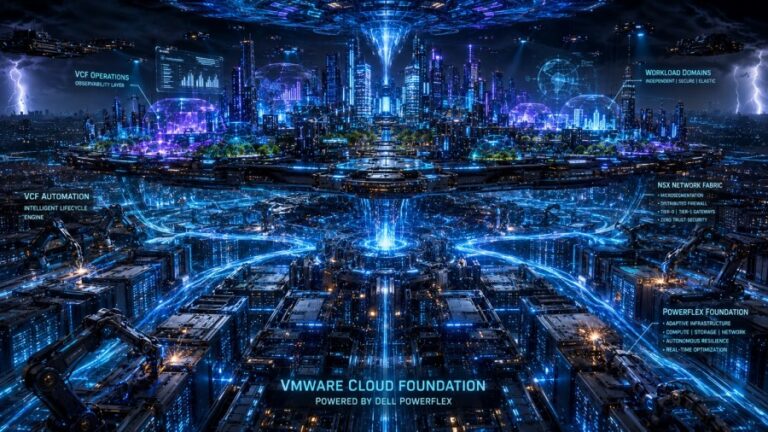
Adding storage or compute capacity can expand the platform, but applications may still require rebalancing, licensing…
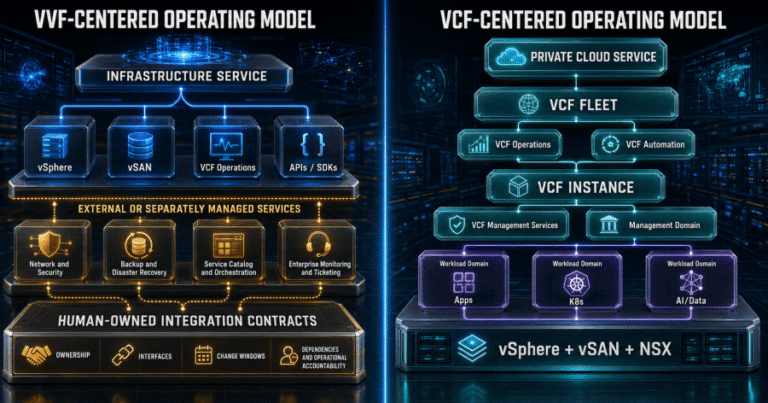
TL;DR The contract should identify a service owner accountable for the complete result. Component specialists retain…
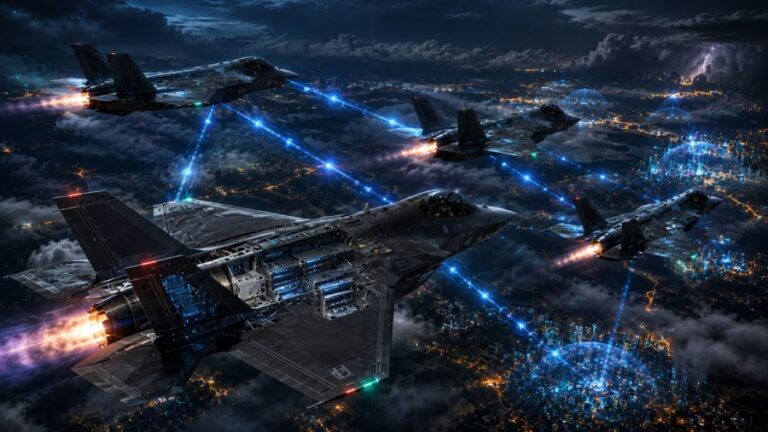
The aircraft in the image are similar, connected, and moving toward a common objective. They are…
When the employee attempted to join the meeting, they almost certainly encountered a fake technical issue…
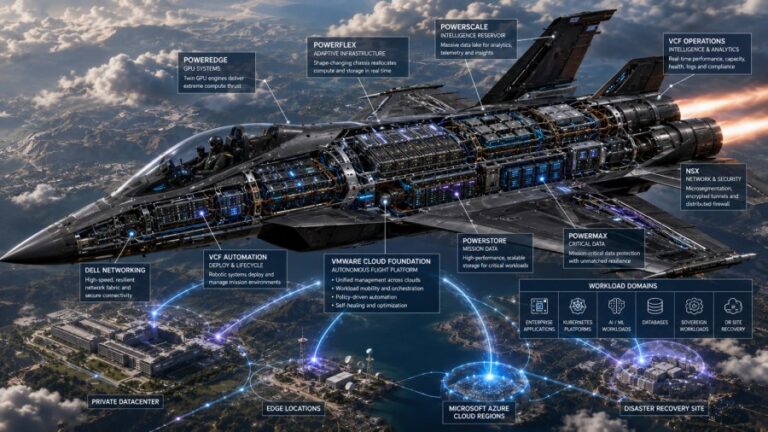
The aircraft mental model is strongest when it exposes integration. It becomes misleading when it hides…
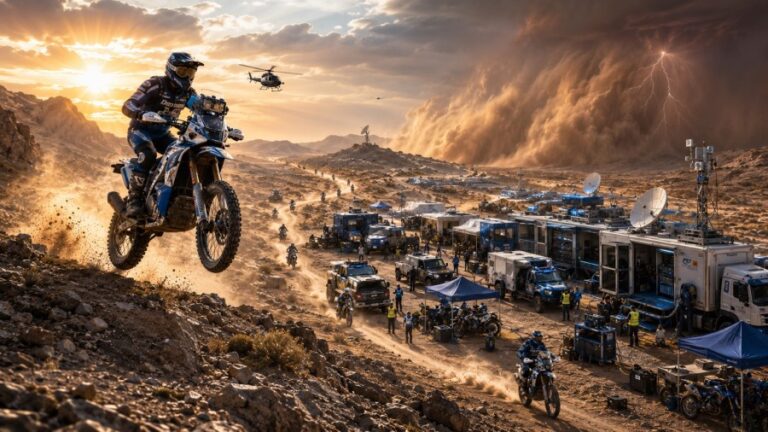
The rally-raid metaphor makes the division of responsibility visible. The rider cannot tow the entire support…
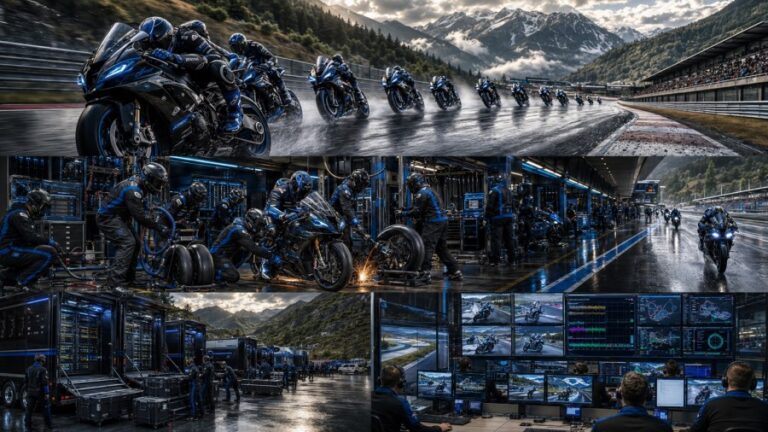
Amber-lane actions are repeatable but need human approval because they affect availability, capacity, identity, security, or…
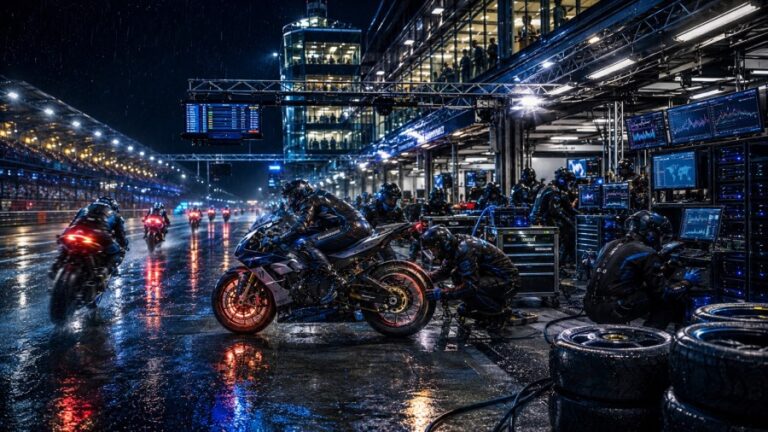
Better approach: Use higher-frequency collection for defined failure modes and critical services where the additional evidence…
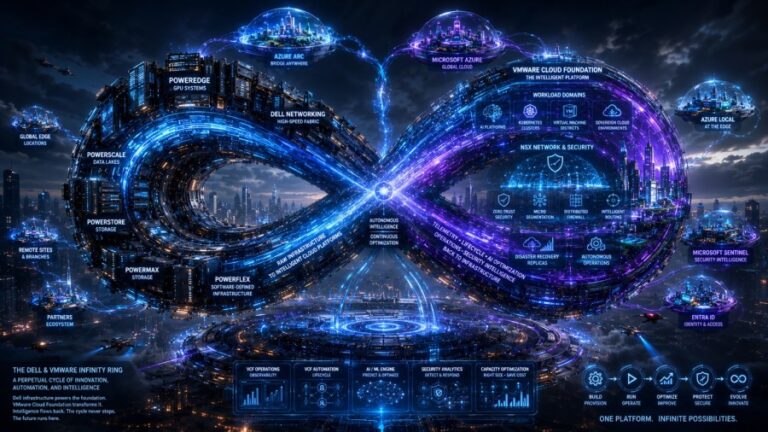
The purpose of this model is not to create bureaucracy. It is to remove the ambiguity…
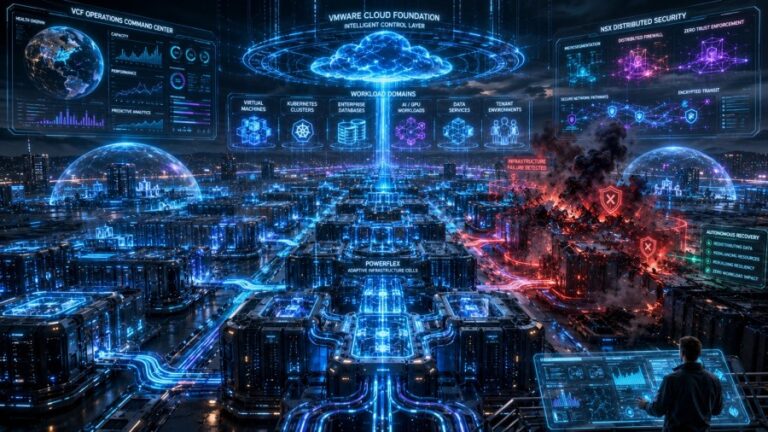
New articles On this page Introduction VCF Operations is the visual command center in the image….
eCrime threat actors will likely continue integrating AI-generated tooling into their operations, as these tools reduce…
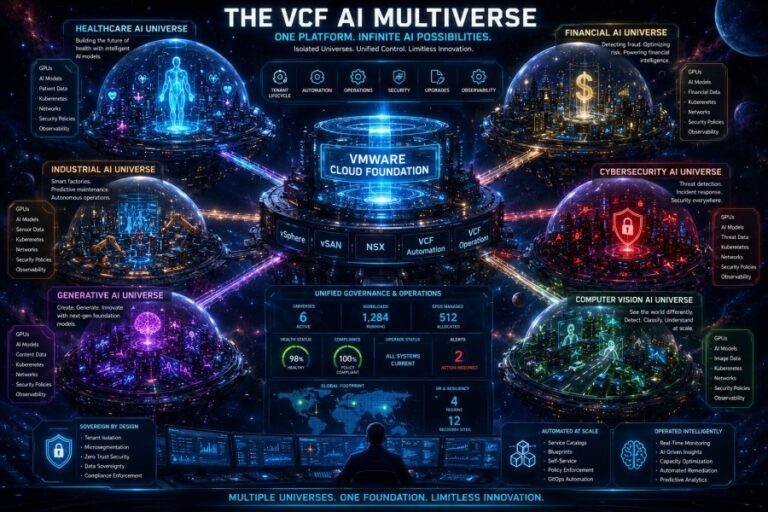
The likely failure mode is false abstraction. A clean profile does not guarantee that every underlying…
September 2026 Attack Surface Overview For a visual overview of the systems impacted by this month’s…
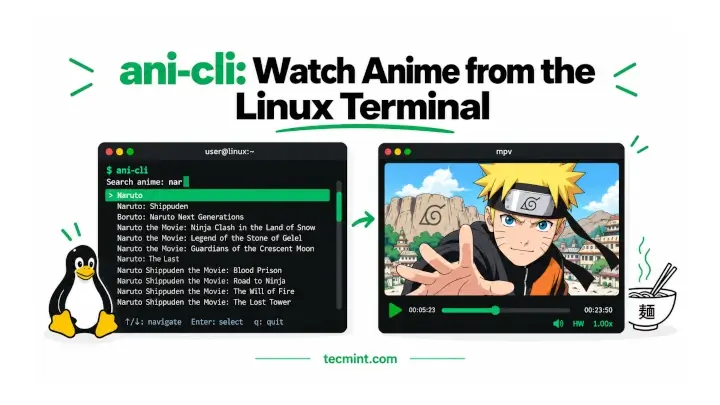
ani-cli is a POSIX shell script that lets you search for anime, choose an episode, and…