CrowdStrike Extends the Agentic SOC to Detect and Stop Agent Insider Threats
Because the context around an agent doesn’t always live inside the Falcon platform, Federated Search Expansion…
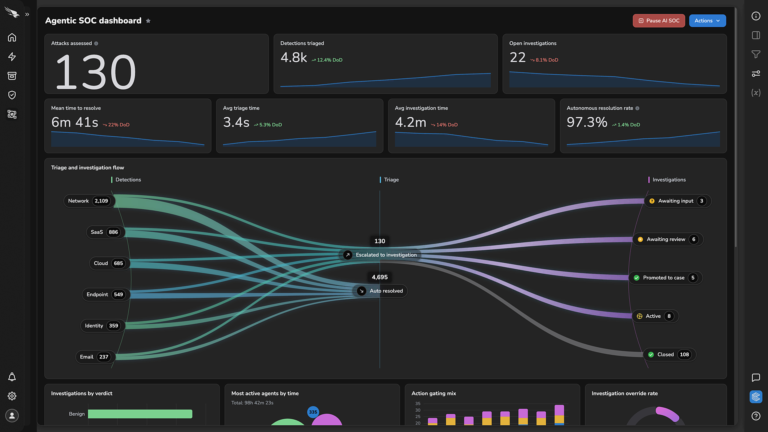
Because the context around an agent doesn’t always live inside the Falcon platform, Federated Search Expansion…
Agent hooks plug into an agent’s native hooks system to capture activity at key points in…
Consider the following hypothetical scenario: A developer may ask their endpoint coding agent: “The integration tests…
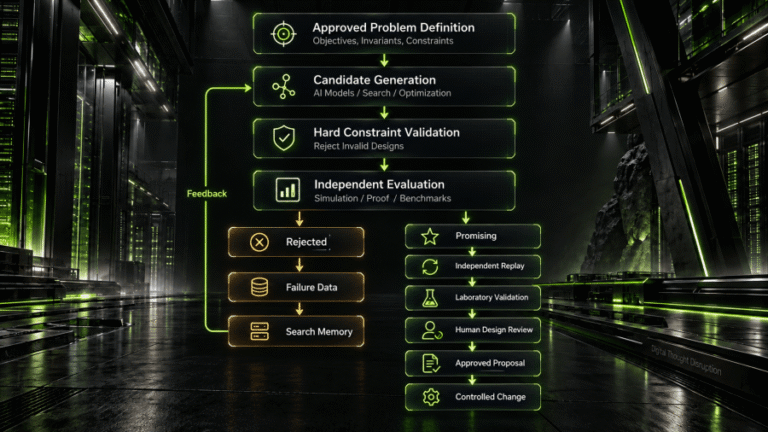
TL;DR Suppose a generated routing strategy reduces measured congestion but introduces difficult configuration dependencies, unclear troubleshooting…
While this activity has not been attributed to a named adversary, the threat actor is likely…
Cross-request semantic accumulation (flagging when an API key’s recent requests jointly cover a harmful-composition template) is…
eCrime threat actors will likely continue integrating AI-generated tooling into their operations, as these tools reduce…
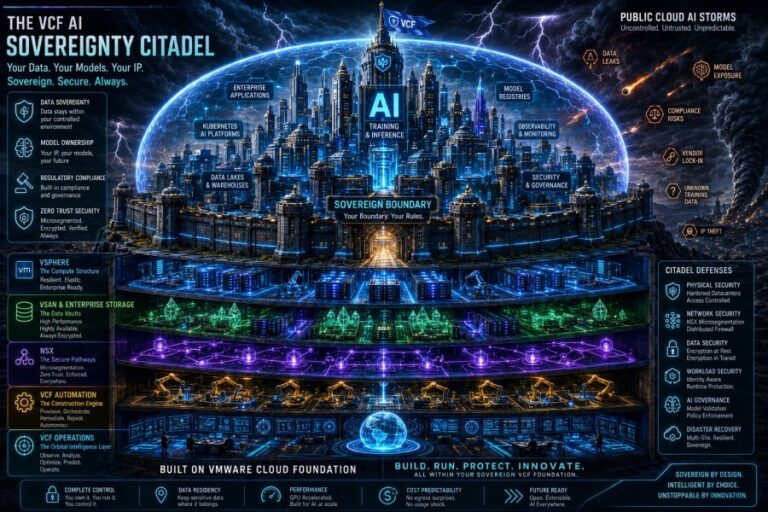
Automation should reject incomplete requests. If a team cannot identify the business owner, data classification, approved…
This 43.0 percentage point increase in high-confidence false positive recall means far more benign alerts can…
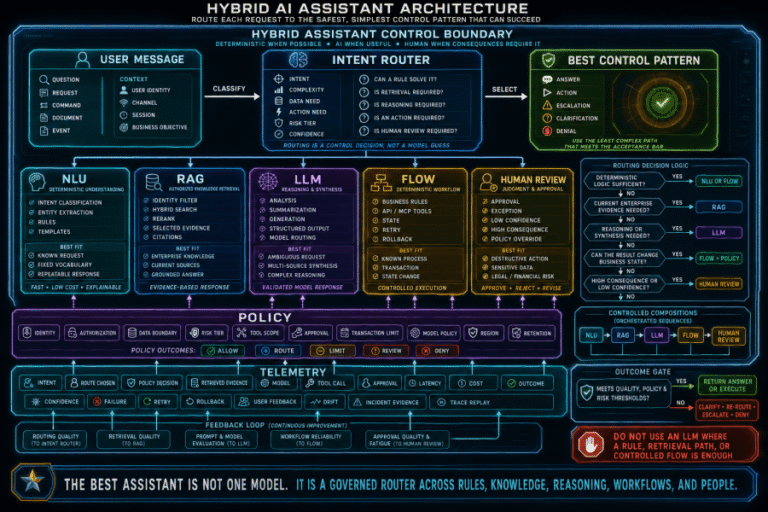
The assistant should retrieve relevant content, generate a grounded response, and provide citations or source references….
Beyond credential harvesting, the worm targets password manager CLIs (bw, op, lpass) and local SQLite stores…
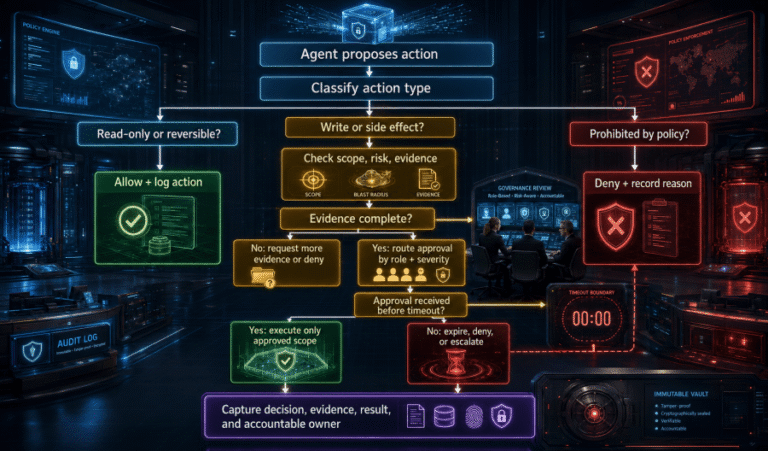
If approval happens too early, the human may approve a general plan before the actual tool…
The new Prompt Injection Taxonomy gives security teams, developers, AI engineers, and red teams a more…

CrowdStrike is redefining identity security with Continuous Identity — delivered through CrowdStrike Falcon® Next-Gen Identity Security…

If you’ve ever tried setting up Ollama, Stable Diffusion, or PyTorch on an AMD graphics card,…