Unknown Threat Actor Uses AI-Driven ARTEX to Target South Korean Finance
While this activity has not been attributed to a named adversary, the threat actor is likely…
While this activity has not been attributed to a named adversary, the threat actor is likely…
Most compose.yaml files slowly turn into long, copy-pasted blocks with fragile startup dependencies. Docker Compose includes…
Cross-request semantic accumulation (flagging when an API key’s recent requests jointly cover a harmful-composition template) is…
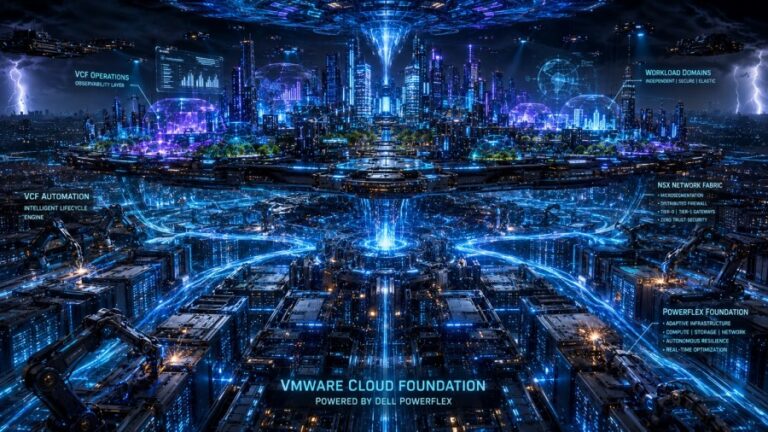
Adding storage or compute capacity can expand the platform, but applications may still require rebalancing, licensing…
For example, following a payment provider breach, customers can identify applications communicating with the provider and…
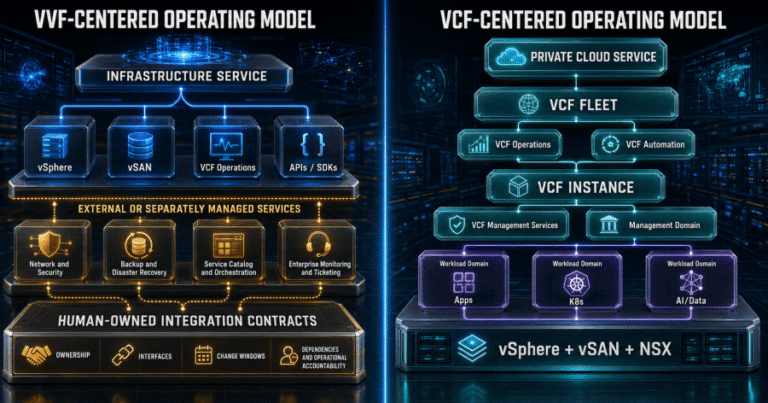
TL;DR The contract should identify a service owner accountable for the complete result. Component specialists retain…
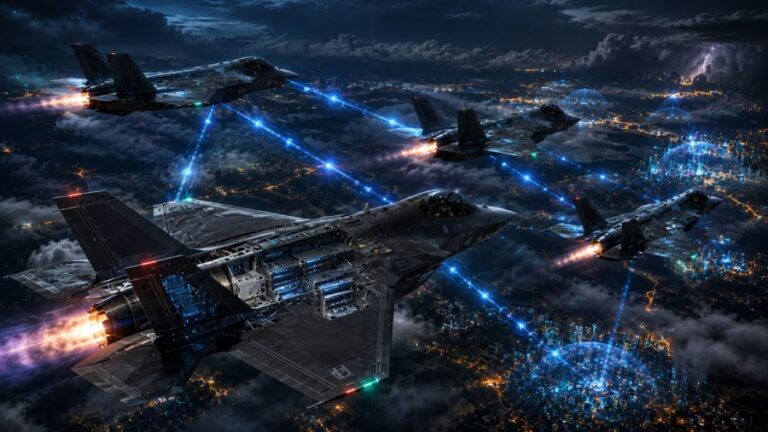
The aircraft in the image are similar, connected, and moving toward a common objective. They are…
AI agents are already operating across the enterprise. As they become more autonomous in accessing data,…
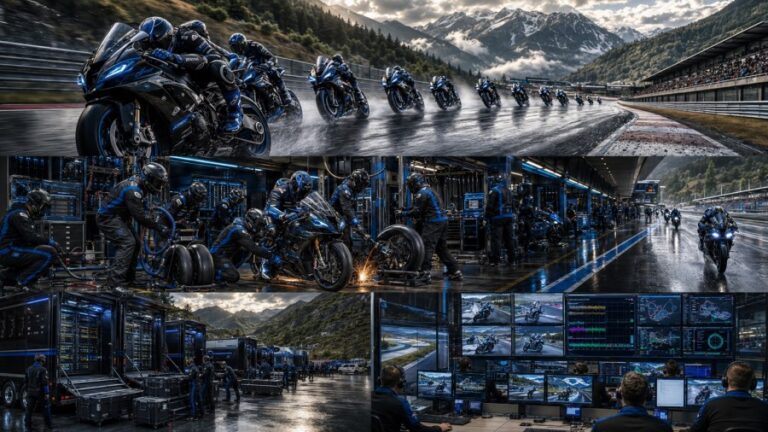
Amber-lane actions are repeatable but need human approval because they affect availability, capacity, identity, security, or…
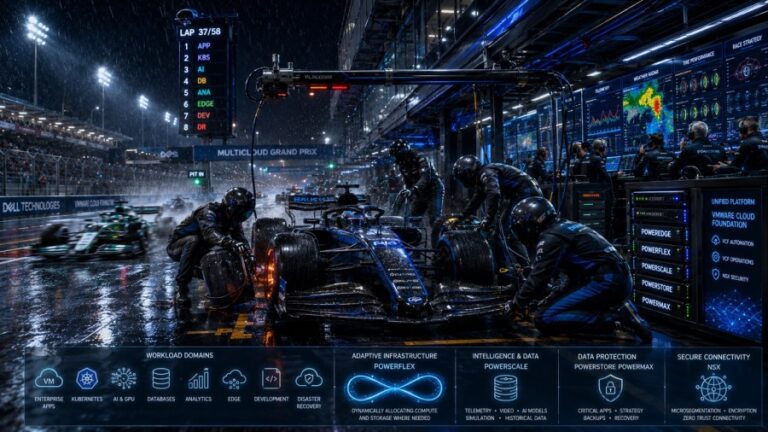
A platform team should not select it merely because the environment includes AI. The decision should…
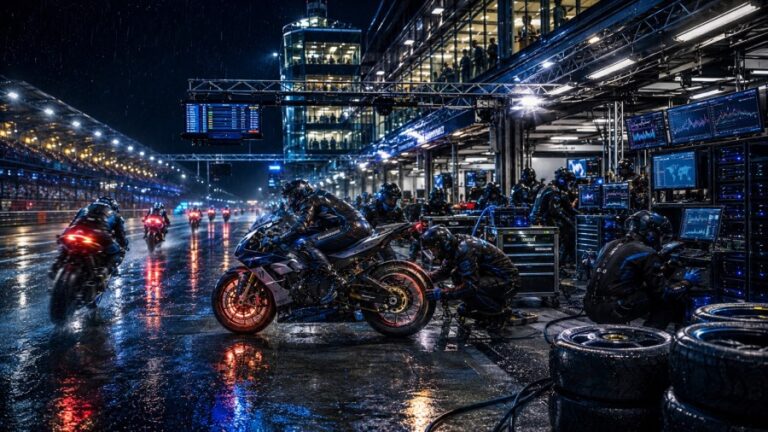
Better approach: Use higher-frequency collection for defined failure modes and critical services where the additional evidence…
The reasoning output should be structured. At minimum, it should include the proposed action, evidence used,…
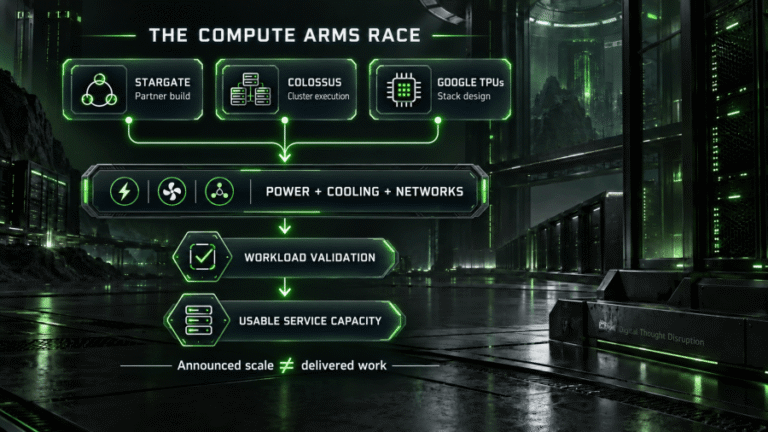
Include porting work, unsupported operations, numerical validation, profiling, release engineering, and the replacement path in the…
eCrime threat actors will likely continue integrating AI-generated tooling into their operations, as these tools reduce…

Build those distinctions into separate records and enforceable transitions. Preserve provenance, bind approvals to immutable action…