Solving the Continuous Authorization Conundrum
To take care of this, organizations often consider two strategies:This brings us to the continuous authorization…
To take care of this, organizations often consider two strategies:This brings us to the continuous authorization…
The program brings together cybersecurity and critical infrastructure leaders with Anthropic’s technical guidance and frontier research…
Flat connectivity, shared administrative credentials, undocumented dependencies, and unrestricted service access erase the benefit of domain…
While this activity has not been attributed to a named adversary, the threat actor is likely…
Advancing Endpoint Security to Face Future Threats We believe the strengths noted by IDC MarketScape reinforce…
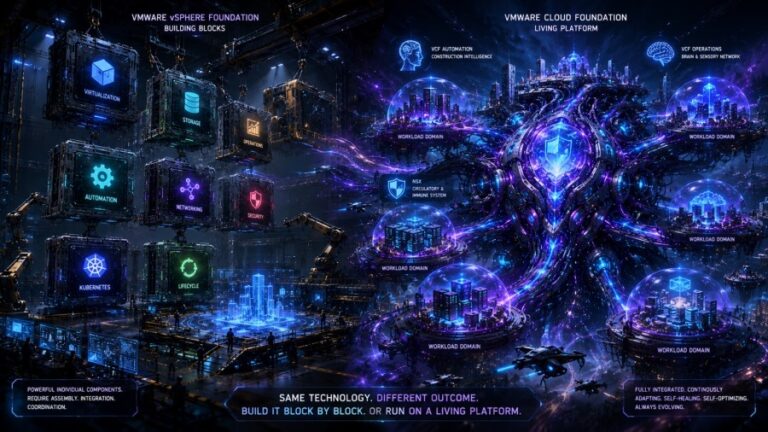
TL;DR A VVF-to-VCF program should earn expansion through one complete service. Establish the current estate, define…
Most compose.yaml files slowly turn into long, copy-pasted blocks with fragile startup dependencies. Docker Compose includes…
Cross-request semantic accumulation (flagging when an API key’s recent requests jointly cover a harmful-composition template) is…
In other words, build a website that is genuinely helpful to people.Together, these resources create a…
A Docker host can run reliably for months and still fill its disk overnight or expose…
Edge servers with 1 GB of RAM and a unreliable, slow uplink need more than a…
Adding storage or compute capacity can expand the platform, but applications may still require rebalancing, licensing…
Discover and Protect Sensitive Data in Microsoft 365 Falcon Data Security for SaaS continuously discovers and…
For example, following a payment provider breach, customers can identify applications communicating with the provider and…
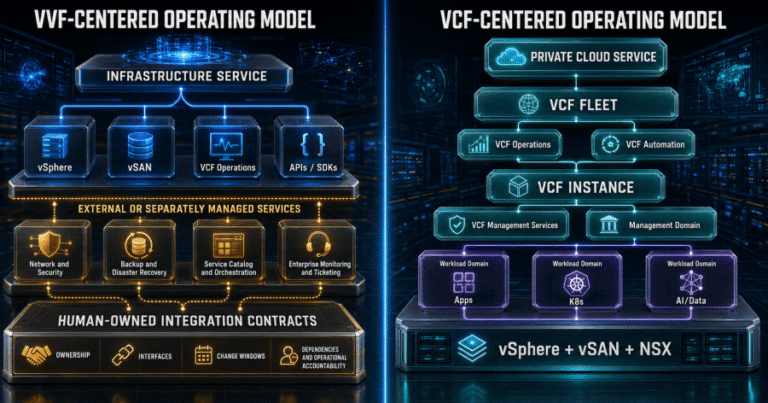
TL;DR The contract should identify a service owner accountable for the complete result. Component specialists retain…