The exit criterion is restored trust, not merely restored service availability.
The decision depends on whether the activity is authorized, consistent with its documented purpose, and supported by reliable evidence.
The reported activity involved multiple malware families, specialized utilities, credential theft, and infrastructure-specific lateral movement.
Security teams should compare activity against approved change records and known administrative behavior.
This is especially relevant to ESX hosts. They may not require a patch for CVE-2026-123890, but their administrative sessions, configuration changes, and sensitive data may still be part of the incident investigation.
Start by identifying every vCenter instance, including those deployed inside VCF management and workload domains, standalone vSphere environments, secondary sites, recovery locations, labs with production connectivity, and environments operated by third parties.
The attack potentially compromised authentication material used to establish trust inside the vSphere environment.
Use tightly defined access policies and enforce them through supported network controls that remain useful even if an individual management appliance is compromised.
Traditional segmentation may separate application workloads from one another. It may protect database networks, application tiers, and tenant environments.
Broadcom confirms that vCenter 8.0 Update 3m and vCenter 9.0.2.0200 block upgrades to VCF 9.1.1.
The problem is that a system can be fully patched today and still contain unauthorized access established yesterday.
| Security characteristic | Confirmed information |
|---|---|
| Vulnerability | CVE-2026-123890 |
| Advisory | VMSA-2026-0009 |
| Publication date | November 19, 2026 |
| Component | VMware vCenter Directory Service |
| Vulnerability class | Authentication bypass |
| CVSS version | 3.1 |
| Severity | 9.8, Critical |
| Attack vector | Network |
| Prior authentication required | No |
| User interaction required | No |
| Broadcom workaround | None |
| Remediation | Install the applicable fixed release |
| Exploitation | Reported in the wild by Google Threat Intelligence Group and Mandiant |
A disaster recovery procedure must consider the possibility that the management plane is not simply unavailable but actively untrusted.
The issue arises when a patched source branch contains a build later than the version expected by the planned upgrade target.
Attackers may rename tools, change infrastructure, use alternative accounts, or operate through otherwise legitimate administrative interfaces.
Understanding the authentication-bypass mechanism
When attackers gain sufficient control over vCenter, they may be able to reach administrative capabilities that extend beyond the original appliance. Access to host administration, virtual machine operations, management credentials, directory information, and authentication infrastructure can turn one compromised control plane into a much larger incident.
A completed patch does not prove that a compromised environment is clean. Conversely, an investigation that finds no evidence of exploitation does not remove the need to patch.
The update introduces a Back-in-Time upgrade restriction for specific source and target combinations.
A useful postchange assessment should demonstrate that the expected software was installed, the management environment remains operational, and any identified security incident has been addressed through the appropriate separate process.
Broadcom’s initial FAQ identifies VCF 9.1.2 as the expected compatible upgrade target. Confirm its availability and the final interoperability matrix before committing an upgrade window. [3]
The advisory identifies VMware Tools 13.1.5.0 as the fix for the 13.x branch and 12.5.5 for affected older supported branches. For 32-bit Windows, VMware Tools 12.4.10 is included in the 12.5.5 release as the relevant fix. [1]
One of the most important discoveries was BONESAW, a purpose-built exploitation utility written in Go.
Broadcom confirms that the vCenter Appliance Management Interface, commonly known as VAMI, can be used for applicable standard update workflows. In an integrated VCF estate, administrators must also respect the applicable VCF lifecycle and support requirements.
The standard supported update mechanism must be used for the relevant platform version and deployment model.
Affected vCenter Versions and Required Fixes
That transition can require stronger containment, forensic preservation, identification of attacker-controlled accounts, assessment of stolen credentials, and validation of the trust material used by vCenter SSO and related services.
Although CVE-2026-123890 is the highest-priority issue in the advisory, VMSA-2026-0009 includes four additional vulnerabilities.
| Platform | Affected vCenter release | Required fixed release |
|---|---|---|
| VMware Cloud Foundation / vSphere Foundation 9.1 | vCenter 9.1.x | 9.1.1.0200 |
| VMware Cloud Foundation / vSphere Foundation 9.0 | vCenter 9.0.x | 9.0.2.0200 |
| VMware vSphere 8.0 | vCenter 8.0 | 8.0 Update 3m |
| VMware Cloud Foundation 5.x | vCenter component | VCF 5.2.5 remediation path, including vCenter 8.0 U3m |
| VMware vSphere 7.0 | vCenter 7.0 | Contact Broadcom Support with an active extended support contract |
| VMware Telco Cloud products | Affected releases identified by Broadcom | Follow product-specific remediation instructions in Broadcom KB 463116 |
For VCF 5.x, do not interpret the reference to VCF 5.2.5 as permission to ignore the underlying vCenter build.
The VCF 5.x distinction matters
CVE-2026-123890 exposes a recurring problem in enterprise infrastructure security: management systems often possess broad authority while being reachable from more locations than their threat model should permit.
Broadcom describes a local privilege-escalation scenario involving an attacker with access to a privileged process inside a Windows guest configured with Guest Alias mapping.
The Mandiant report provides a useful starting point for hunting because it describes a sequence of attacker behavior rather than only a vulnerability identifier.
The observed capabilities should not be treated as proof that every payload behaves identically on every vulnerable release. However, the vendor’s affected-version matrix requires immediate attention regardless of which release was involved in the observed incident.
What about older vSphere installations?
VMware vSphere 7.0 has passed general support and requires the relevant extended-support arrangement to obtain a supported security response.
The disclosure becomes more significant when viewed against the timeline published by Google Threat Intelligence Group and Mandiant.
Neither approach should be interpreted as permission to leave a vulnerable management plane broadly exposed while waiting for a preferred upgrade milestone.
Exploitation Was Confirmed Before Public Disclosure
Patch the vulnerability. Investigate the control plane. Re-establish trust where necessary. Then prove the environment is operationally and administratively secure.
More concerning, Google Threat Intelligence Group and Mandiant have confirmed that the suspected PRC-linked threat actor ARMORY CASTLE exploited the vulnerability as a zero-day in early September 2026. The reported attack involved a purpose-built tool called BONESAW, unauthorized vCenter administrative access, directory database extraction, compromised identity material, and subsequent activity targeting the underlying virtualization environment. [2]
Get Paul Bryant’s practical guides to enterprise AI, hybrid platforms, and day-2 operations by email. New articles as they publish. Unsubscribe anytime.
Broadcom’s supplemental FAQ directs VCF 5.x customers to apply the vCenter 8.0 Update 3m remediation through the supported asynchronous patching process described in KB 88287 and to update SDDC Manager to 5.2.5.
[3] VMware by Broadcom, “VMSA-2026-0009: Questions & Answers,” initial advisory supplement, Nov. 19, 2026. [Online]. Available: https://github.com/vmware/vcf-security-and-compliance-guidelines/blob/main/security-advisories/vmsa-2026-0009/README.md. Accessed: Nov. 19, 2026.
BONESAW and the compromise of vCenter identity
For an enterprise already upgrading from VCF 5.x or 9.0 toward VCF 9.1.1, that creates a scheduling and sequencing decision.
Consider an enterprise running VMware Cloud Foundation across multiple sites. Its vCenter instances manage ESX hosts, virtual machines, administrative permissions, configuration changes, and integrations with the surrounding infrastructure ecosystem.
Once this administrative access is obtained, the consequences can extend to directory service operations, sensitive database access, credential material, and other privileged functions.
It is important to separate two statements: Broadcom confirms the broad authentication-bypass exposure across the affected versions, while Mandiant’s investigation documents specific post-exploitation capabilities, including full system compromise involving vCenter 7.x and 8.x appliances.
Organizations operating integrated or engineered infrastructure, including vendor-qualified platforms such as VxRail, must also respect the applicable engineered-system support and release qualification process rather than assuming a standalone appliance patch procedure is automatically appropriate.
For affected customers, the decision belongs in a coordinated review involving security, platform architecture, lifecycle engineering, and the accountable change authority.
For each instance, record the actual installed version and build, supported upgrade path, management-network exposure, responsible platform owner, and applicable maintenance constraints.
The vulnerability affects the Secure Remote Password authentication mechanism, specifically SRP-6a, exposed through the VMware Directory Service’s Distributed Computing Environment/Remote Procedure Call interface.
The attack was not the same as the earlier vCenter vulnerability
Treat vCenter SSO, local appliance accounts, service credentials, tokens, certificates, and signing material as critical enterprise security assets.
The correct operating response combines emergency patch deployment, targeted compromise assessment, controlled containment, supported lifecycle planning, and evidence-based recovery.
Broadcom’s advisory identifies CVE-2026-123890 as an authentication-bypass vulnerability in the VMware Directory Service used by vCenter. [1]
A clean vCenter health status cannot prove that credentials were never stolen. An operational ESX cluster cannot prove that administrative access was not abused. A successful login does not establish that the SSO trust chain has remained uncompromised.
A practical investigation should connect identity changes, management access, appliance activity, and downstream host operations.
The Real Security Boundary Is the Management Plane
That should not be interpreted as zero operational impact.
The organization has invested in backup, network segmentation, privileged access management, and operational monitoring. Individual application workloads may be properly secured, and administrative access to the vSphere Client may require strong authentication.
Do not delay necessary containment indefinitely to perfect evidence collection. The incident commander and platform owner need an agreed sequence that balances preservation with continuing exposure.
These fixed-release references are based on the initial Broadcom advisory and supplemental FAQ dated November 19, 2026. [1] [3]
The harder work is establishing whether a vulnerable vCenter was accessed before the patch, whether attackers obtained persistent administrative access, and whether sensitive identity or signing material can still be trusted.
Three affect SDDC Manager, while the fourth affects VMware Tools for Windows. [1]
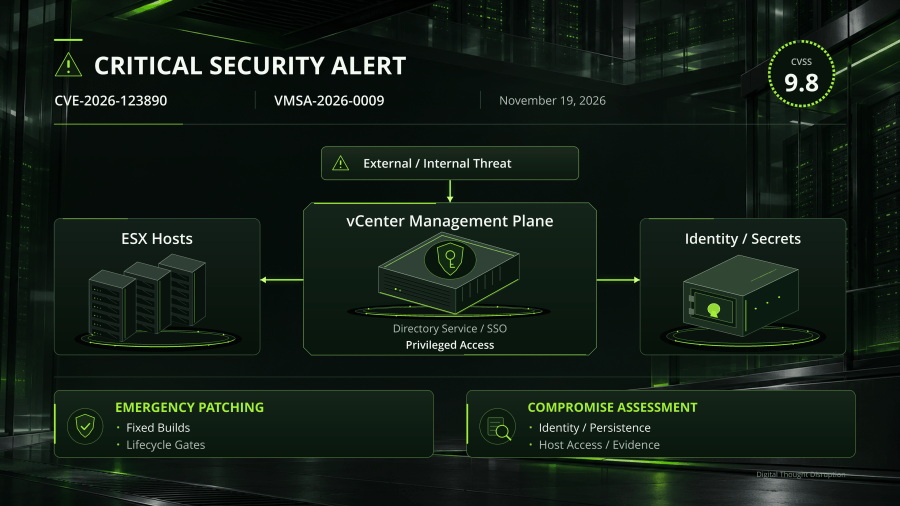
Broadcom’s November 19, 2026 disclosure of CVE-2026-123890 is a critical VMware security event because the weakness affects a highly privileged control plane and has already been exploited in the wild.
Where an appliance is suspected of compromise, coordinate evidence collection and administrative access with incident responders before performing routine interactive administration.
That introduces a materially different recovery requirement from a conventional stolen-password incident.
On November 19, 2026, Broadcom published VMSA-2026-0009, disclosing five vulnerabilities affecting VMware vCenter, SDDC Manager, and VMware Tools for Windows. The most serious, CVE-2026-123890, is a critical authentication-bypass vulnerability in the VMware vCenter Directory Service with a CVSS 3.1 score of 9.8. An unauthenticated attacker with network access to the vulnerable service can bypass authentication and obtain unauthorized access to vCenter. Broadcom has released fixes and documents no workaround. [1]
| Workstream | Immediate objective | Completion evidence |
|---|---|---|
| Vulnerability remediation | Identify and patch affected vCenter instances | Installed fixed builds and successful platform validation |
| Compromise assessment | Investigate possible exploitation and persistence | Documented investigation across identity, appliance, host, and network evidence |
| Containment | Reduce attacker access while remediation proceeds | Verified management-network restrictions and privileged-access controls |
| Trust recovery | Remove unauthorized access and re-establish trustworthy identity | Validated accounts, credentials, signing material, and administrative access |
| Operational recovery | Restore the approved platform operating state | Verified management functions, monitoring, backup, and recovery capability |
Administrative tools, monitoring platforms, automation services, backup appliances, and remote support infrastructure can all accumulate legitimate connectivity requirements.
Management-network access should not be broadly inherited by ordinary application servers, remote-access appliances, or shared administrative networks.
Establish a reliable inventory
Continue reading
Where the integrity of the management appliance cannot be established, recovery from a validated trusted state may be preferable to treating an in-place patch as a complete remediation.
This distinction matters when evaluating whether a particular component is already protected. The vCenter and SDDC Manager fixed-version requirements should not be conflated simply because the components are part of the same VCF deployment.
One addresses the vulnerable software.
The distinction is between a product containing the disclosed vulnerability and a product potentially exposed to an attacker who has already compromised its administrative infrastructure.
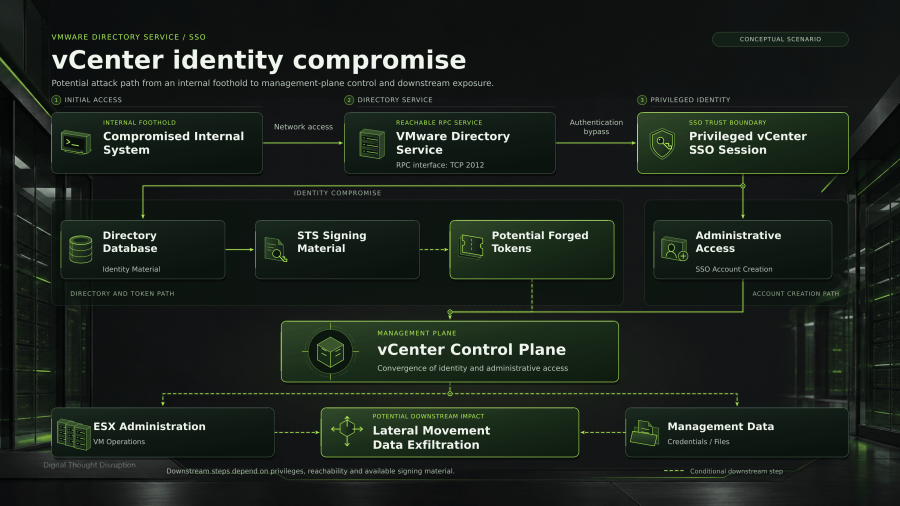
The investigation identifies TCP port 2012 as an important interface in the observed exploitation.
Restrict management-plane connectivity
Administrative privileges should be limited, reviewed, and monitored. Emergency access should be available without depending entirely on the identity service being investigated.
The other determines whether the trust boundary has already been crossed.
A newly created administrative account might belong to a legitimate automation project. An SSH configuration change might have been approved for troubleshooting. Neither is inherently malicious.
Broadcom’s FAQ discusses both waiting for the compatible future target and accelerating the move to a newer vCenter release before applying the relevant security update.
Broadcom’s FAQ also warns that older, out-of-support releases such as vSphere 6.5 and 6.7 are not evaluated as part of current security advisories. Administrators should not conclude that an unlisted, unsupported version is safe. [3]
Use the actual installed version and build, not merely the platform’s marketing release or the version recorded in an outdated configuration management database.
This is not a guest-to-host escape.
A backup that can restore an appliance is valuable. A recovery procedure that can restore a trustworthy management environment is more valuable.
Preserve useful evidence before destructive changes
The maintenance plan should reflect those dependencies rather than treating the update as an isolated appliance restart.
Over time, that can create a large attack surface around the most privileged systems in the environment.
The completion criteria need to cover both technical functionality and security state.
Any appliance-local firewall hardening or other nonstandard modification must also be evaluated for vendor supportability and operational impact before production deployment.
The previous fix does not eliminate the need for VMSA-2026-0009.
What Security Teams Should Investigate
The operational takeaway: this is an emergency management-plane security event, not simply another patching exercise. VMware and VMware Cloud Foundation customers need to establish which systems are vulnerable, deploy the correct fixes, investigate evidence of prior compromise, and evaluate whether their identity and administrative trust boundaries remain intact. Patching closes the disclosed vulnerability, but it does not automatically revoke malicious accounts, invalidate stolen signing keys, or remove attacker persistence.
The November 19 advisory is especially significant because the vulnerability was exploited before public disclosure.
| Investigation area | Evidence worth examining | Why it matters |
|---|---|---|
| vCenter SSO | Unexpected administrator accounts, privilege assignments, account creation, authentication activity | May identify unauthorized privileged access |
| Directory Service | Suspicious database access, directory changes, unexpected privileged operations | May indicate identity information theft or manipulation |
| STS and SAML trust | Signing-material exposure, unusual token issuance, unexpected administrative sessions | May indicate token forgery or compromised trust material |
| vCenter appliance | Unauthorized SSH enablement, new local accounts, unfamiliar processes, unexpected file access | May indicate persistence or appliance-level compromise |
| ESX administration | Unexplained administrator sessions, SSH changes, host configuration changes | May indicate movement from vCenter into the host estate |
| Network telemetry | Connections to sensitive management interfaces, unusual management traffic, unexpected outbound transfers | May identify reconnaissance, exploitation, or exfiltration |
| Adjacent appliances | Unrecognized tools, scheduled tasks, service changes, suspicious privileged activity | May identify staging or lateral movement outside vCenter |
Mandiant reports that BONESAW was used against a vCenter system that had already received remediation for CVE-2026-59309.
For the broader recovery sequence, see Cyber Recovery After Management-Plane Compromise. For longer-term containment design, see Designing VCF, Azure Local, and Nutanix for Persistent Compromise.
That changes the risk calculation.
Organizations should review which systems can reach this service and whether that access is operationally necessary.
Mandiant describes a broader intrusion in which attackers first compromised remote-access infrastructure, established control over internal Linux appliances, and subsequently targeted VMware management systems.
What to do if compromise is suspected
The weakness does not require the attacker to know an administrator’s password. It does not require a legitimate user session. The authentication process itself can be bypassed.
The goal is to select an approved path that satisfies both the immediate security requirement and the platform’s supported upgrade sequence.
A vulnerability affecting an application server is serious. A vulnerability affecting the management platform responsible for administering hundreds or thousands of application servers creates a different security problem.
These activities are related, but their exit criteria are different.
The objective is to help architects, platform engineers, and security leaders make a defensible response decision without confusing a successfully installed patch with proof that the environment is trustworthy.
Mandiant describes a cryptographic logic and authorization weakness involving the rpc_srp_verifier service, enabling an attacker to obtain session-key material without knowing the legitimate password. [2]
For CVE-2026-123890, the response should therefore operate through two coordinated workstreams.
Additional Vulnerabilities Affecting VMware Cloud Foundation
The vulnerability concerns vCenter rather than a guest-to-hypervisor escape. Broadcom’s supplemental FAQ explicitly distinguishes this issue from a VM escape and confirms that ESX itself is not directly affected by this particular advisory. [3]
Those are separate questions requiring separate evidence.
| CVE | Component | Issue | CVSS 3.1 |
|---|---|---|---|
| CVE-2026-123890 | vCenter | Directory Service authentication bypass | 9.8 |
| CVE-2026-123891 | SDDC Manager | SQL injection | 8.1 |
| CVE-2026-123892 | SDDC Manager | Authenticated command injection | 7.2 |
| CVE-2026-123893 | SDDC Manager / VCF Installer | Local privilege escalation | 6.7 |
| CVE-2026-123894 | VMware Tools for Windows | SAML token signature bypass | 6.7 |
The security model should therefore be reviewed across three dimensions.
SDDC Manager remediation
administrator@vsphere.local
| VCF release | SDDC Manager fixed version |
|---|---|
| VCF 9.1.x | 9.1.1.0200 |
| VCF 9.0.x | 9.0.2.0100 |
| VCF 5.x | 5.2.5 |
One of the most consequential operational details in Broadcom’s supplemental FAQ is the interaction between these security patches and ongoing VMware Cloud Foundation upgrades.
This article examines the verified vulnerability, affected releases, reported attack behavior, emergency remediation process, compromise-assessment requirements, and additional VMware Cloud Foundation lifecycle considerations.
VMware Tools for Windows
When an attacker obtains signing keys or other privileged identity material, removing a suspicious account may not be sufficient. The attacker may retain another mechanism for impersonating trusted identities.
For the SDDC Manager vulnerabilities, Broadcom lists the following fixed versions in the November 19 response matrix.
Mandiant’s investigation identifies TCP 2012 as a key part of the observed attack path.
[4] Broadcom, “Applying individual product updates to VMware Cloud Foundation environments using Async Patch,” Knowledge Base, Art. 344935 (legacy KB 88287). [Online]. Available: https://knowledge.broadcom.com/external/article/344935. Accessed: Nov. 19, 2026.
According to their November 19 investigation, the suspected PRC-nexus threat actor ARMORY CASTLE, previously tracked as UNC5221, exploited CVE-2026-123890 in early September 2026. [2]
What is not directly affected?
An attacker does not necessarily need a vulnerability in the hypervisor to affect the hypervisor estate when a compromised management platform already has administrative capabilities over it.
Broadcom’s supplemental FAQ confirms that VMware ESX, NSX, VCF Operations, and VCF Automation are not directly affected by the vulnerabilities in this advisory. [3]
Mandiant reported that SAWSNAKE could use extracted signing material to forge SAML assertions and obtain administrative session cookies. [2]
The management plane should be treated as critical infrastructure in its own right, because when its identity and authority are compromised, the consequences may extend to everything it manages.
That does not remove the need to review those systems when investigating an actual vCenter compromise.
VCF 9.1 introduced vCenter Quick Patch capability for applicable update scenarios.
Both component state and supported lifecycle sequencing matter. The asynchronous patching process does not always mean using the Async Patch Tool. KB 88287 directs VCF 5.2 and 5.2.1 environments to the in-product Flexible BOM workflow for applicable patches. Check the current patch-specific row and platform guidance before choosing the tool. [4]
A routine vCenter update generally does not stop running virtual machines. Broadcom’s FAQ confirms that workloads continue while vCenter management services are temporarily unavailable. [3]
Those facts give organizations a clear starting point.
Mandiant observed the attackers using BONESAW to obtain privileged vCenter access, extract the underlying VMware Directory Service database, and establish additional administrative access.
| Situation | Operational implication |
|---|---|
| Existing vCenter 9.1.x estate | Apply the fixed vCenter 9.1.1.0200 update using the supported path |
| vCenter 8.0 estate planning VCF 9.1.1 | Applying 8.0 U3m creates the documented Back-in-Time restriction |
| vCenter 9.0 estate planning VCF 9.1.1 | Applying 9.0.2.0200 creates the documented restriction |
| Upgrade program affected by the restriction | Replan the approved sequence, potentially using VCF 9.1.2 when available |
| Upgrade program considering vCenter-first movement | Validate the supported path, interoperability, dependencies, and the final security build before execution |
The broader management-network review should include vCenter administration interfaces, appliance management, SSH, directory services, privileged jump systems, backup infrastructure, and the integrations that rely on management-plane communication.
An estate inventory should therefore capture unsupported systems as explicit security and lifecycle risks, not silently exclude them from the response.
If the investigation identifies credible evidence of unauthorized administrative access, the organization should move from vulnerability response into its formal incident-response process.
[1] Broadcom, “VMSA-2026-0009: VMware vCenter, Tools, and SDDC Manager updates address multiple vulnerabilities,” Nov. 19, 2026. [Online]. Available: https://support.broadcom.com/web/ecx/support-content-notification/-/external/content/SecurityAdvisories/0/39495. Accessed: Nov. 19, 2026.
Why vCenter Quick Patch Is Not the Answer Here
Mandiant’s technical investigation provides more detail than the Broadcom advisory.
Security teams should preserve available evidence from the relevant time period, ideally including logs preceding the earliest known exploitation activity.
However, Broadcom explicitly states that the vCenter updates associated with VMSA-2026-0009 are not eligible for vCenter Quick Patch. [3]
$global:DefaultVIServer.Version
$global:DefaultVIServer.Build
Then a critical vulnerability appears in the directory service supporting the management plane.
The organization may need to restore administrative authority, rebuild affected identity services, validate control-plane integrations, and only then authorize normal infrastructure management.
The normal instinct during an emergency advisory is to identify the vulnerable systems, approve a change, install the patch, and verify the versions.
Nevertheless, organizations should include affected Windows virtual machines in their remediation planning rather than limiting the response exclusively to management appliances.
Broadcom’s supplemental FAQ identifies the vSphere Client Summary tab and PowerCLI as methods for retrieving version and build information. [3]
The key details are straightforward.
Restoring an older appliance image is not automatically a safe response either. A backup may preserve the same vulnerability or attacker persistence, and an older restore point may invalidate later identity or inventory changes.
That means operations teams should not assume the emergency fix can be applied through the faster Quick Patch process.
[2] Google Threat Intelligence Group and Mandiant, “ARMORY CASTLE Exploits vSphere,” Google Cloud Blog, Nov. 19, 2026. [Online]. Available: https://cloud.google.com/blog/topics/threat-intelligence/armory-castle-exploits-vsphere. Accessed: Nov. 19, 2026.
| Validation domain | Required evidence |
|---|---|
| Version compliance | Actual vCenter and relevant SDDC Manager versions match the applicable fixed baseline |
| Platform services | Required vCenter services, inventory, APIs, and authentication operate correctly |
| Host connectivity | ESX hosts and clusters reconnect and report expected operational state |
| Management integration | VCF lifecycle services, NSX integrations, automation, and monitoring operate as expected |
| Identity integrity | Privileged accounts, permissions, sessions, and trust material have been reviewed |
| Security investigation | Findings, evidence gaps, unresolved risks, and incident disposition are documented |
| Recovery readiness | Required management backups and supported recovery procedures are available |
| Network controls | Management-plane access restrictions remain enforced and are documented |
| Lifecycle compatibility | Future VCF upgrade plans reflect the new source builds and known restrictions |
But if an attacker can access a privileged management service from a compromised internal system, the management plane may provide a route around those workload-level boundaries.
This matters for organizations that previously completed emergency vCenter patching and believe they are protected because an earlier directory-service vulnerability was addressed.
If STS signing material was exposed, simply resetting the administrator@vsphere.local password cannot be assumed to invalidate every attacker-controlled authentication mechanism.
The Longer-Term Architecture Lesson
A vCenter compromise can have consequences far beyond a single management appliance.
The significance is not simply that the attackers obtained an administrator account.
During the update, administrative interfaces and dependent management operations can be interrupted. Certain encryption and key-management operations, automation workflows, backup integrations, monitoring processes, and activities requiring live vCenter access may be affected.
The first operational decision is whether each vCenter instance is vulnerable and which supported remediation path applies.
Mandiant’s publication includes network and file indicators, along with detection material. Those indicators should be incorporated into the organization’s threat-hunting process, but matching known indicators is not the only way to identify compromise. [2]
Management-plane isolation
Stay informed
These restrictions are compensating security controls. Broadcom documents no workaround for CVE-2026-123890, and the restrictions do not replace the required fixed releases.
Identity and privileged access
Both concern authentication weaknesses in VMware Directory Service, but their affected interfaces and exploitation mechanisms differ.
The investigation also describes SAWSNAKE, another utility used to manipulate Security Assertion Markup Language (SAML) authentication and generate administrative sessions.
Recovery of trusted control
Successful exploitation can establish an authenticated administrative session as:
Broadcom also clarifies that some SDDC Manager vulnerabilities were resolved in earlier 9.1 releases. CVE-2026-123891 and CVE-2026-123892 were first addressed in 9.1.0.0, while CVE-2026-123893 was addressed in 9.1.1.0. [1] [3]
That includes central security monitoring, vCenter events, SSO administrative activity, privileged-access records, network flow data, remote-access systems, backup infrastructure, and host management activity.
That workflow remains necessary.
Conclusion
This was not a theoretical vulnerability demonstrated only in a research environment.
The following diagram summarizes the relevant trust relationships in the attack described by Mandiant. It is a simplified conceptual sequence, not a claim that every vulnerable installation experienced all these actions.
The preferred control is to restrict access to approved administrative and infrastructure systems at supported network enforcement points, using explicit source and destination rules.
A secure application segment does not automatically compensate for an exposed management-plane identity service.
For VMware Cloud Foundation customers, the response also has to respect management-component dependencies, conventional vCenter patching requirements, integrated platform qualification, and the Back-in-Time upgrade restriction affecting certain VCF 9.1.1 upgrade paths.
Do not assume that removing internet exposure is sufficient. The observed attacker moved laterally from already-compromised internal infrastructure.
CVE-2026-123894 involves VMware Tools for Windows and requires a more specific attack condition.
The vulnerabilities have different prerequisites and security consequences. They should not all be described as unauthenticated remote compromises.
Continue Reading
A mature VMware environment may have extensive workload microsegmentation but comparatively permissive management-network access.
External References
The fixed releases are available, the affected-version boundaries are documented, and Broadcom provides a supplemental FAQ addressing remediation, product impact, and upgrade compatibility.
For VMware Cloud Foundation architects, this reinforces the need to evaluate management-network access separately from application networking.
This creates several practical prechange requirements.
Where logs are missing, expired, or potentially altered, report the resulting visibility gap. Absence of a recorded indicator is not equivalent to proof that an attacker never accessed the environment.